Malware removal & recovery
Full scan and clean of files and database, removal of injected content and backdoors, then blacklist removal with Google and your host once the site is verifiably clean.
Protect · Security
Most hacked WordPress sites were not targeted — they were found by a script scanning for a plugin vulnerability that had a patch available for months. We clean up the damage, close the way in, and put monitoring in place so the next attempt is caught rather than discovered.
That is what our WordPress security work is built to fix.
● Site hacked right now?
Send us the URL and we will start triage immediately. Emergency cleanups are prioritised ahead of scheduled work.
Get emergency help ↗︎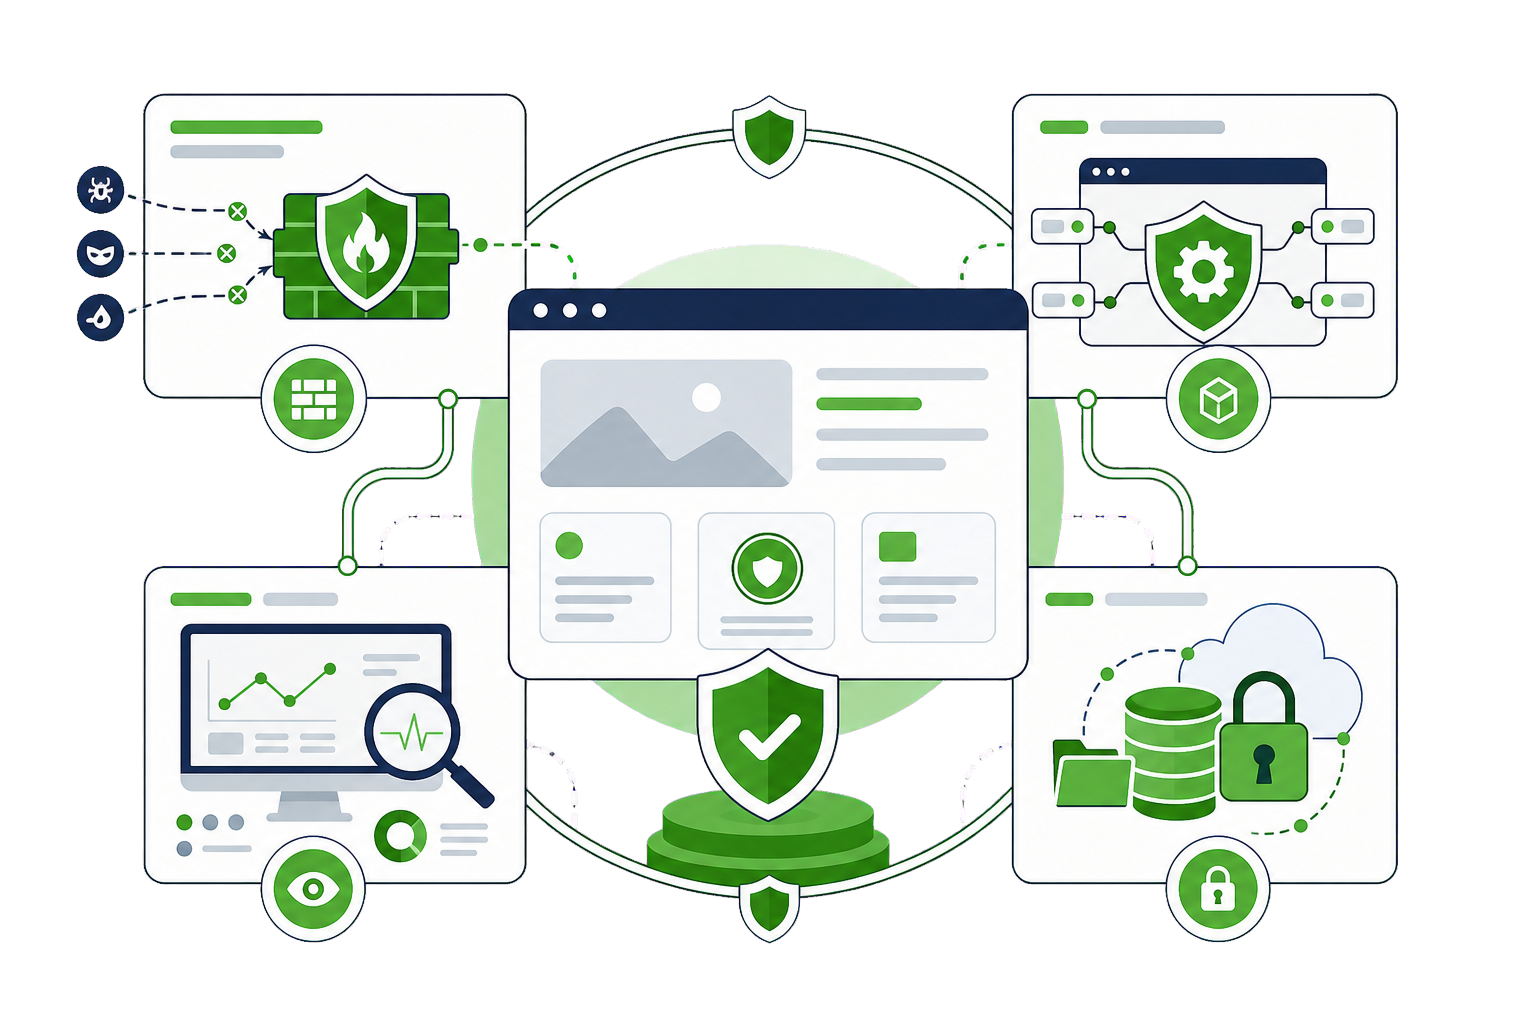
The problem
Spam pages in Google, redirects to somewhere unpleasant, or a warning from your host. The site is still serving customers and every hour it stays infected costs you more trust.
A red interstitial in front of your site, or a manual action in Search Console. Traffic has collapsed overnight and the warning stays until someone cleans the site and requests review.
Someone cleaned the files last time but never found how the attacker got in, or left the backdoor they planted. Reinfection within weeks almost always means the entry point was never closed.
Nothing has gone wrong yet. Nobody can tell you which plugins have known vulnerabilities, whether backups actually restore, or who still has an administrator account from three agencies ago.
What we do
Full scan and clean of files and database, removal of injected content and backdoors, then blacklist removal with Google and your host once the site is verifiably clean.
Finding how they actually got in — logs, file timestamps, user accounts and known vulnerabilities. Cleaning without this is how sites get reinfected within weeks.
File permissions, disabled file editing, restricted PHP execution, forced strong passwords and two-factor authentication, plus a proper review of who holds administrator access.
A web application firewall tuned to your site, with rate limiting on login and XML-RPC and rules for the automated scanning that makes up most of the noise.
Continuous checks against vulnerability databases for every plugin, theme and core version you run, with file integrity monitoring and alerts when something changes unexpectedly.
Offsite, versioned backups that are tested by actually restoring them. A backup nobody has ever restored is not a backup, it is an assumption.
How it works
Limit the damage and stop active malicious behaviour while we investigate.
Remove malware, injected content and backdoors from files and database.
Establish the entry point, because cleaning without this invites reinfection.
Verify the site is genuinely clean and get blacklist warnings lifted.
Close the way in and everything else like it, not just the one hole.
Alerts, integrity checks and vulnerability tracking so the next attempt is caught.
Results
Global Exclusive Movers
Both of the client's sites went dark on the same morning — one showing a Cloudflare 522, the other a connection timeout. The assumption on the table was malware, and a bot flood had been hitting the server that day. Read the Apache logs instead of guessing. There were 48 minutes with zero entries across every domain on the account — requests never reached the server at all. Core checksums passed on all three…
Capabilities
Engagement
Fixed fee
For sites that are compromised right now. Triage begins the same day: clean the infection, find the entry point, close it and get blacklist warnings lifted.
Fixed fee
A written assessment of your current exposure — plugin vulnerabilities, access control, backup viability and hardening gaps, with fixes prioritised by real risk.
Monthly
Firewall management, vulnerability monitoring, tested backups and patching, so problems get handled before they become incidents.
Cost
The engagement shapes above say how the work is bought. This is the other half: why security work on two WordPress sites can be priced very differently, and why the cheapest quote is often for a different, smaller job.
Hardening a healthy site is planned work. Cleaning an active infection is urgent work with an unknown scope: every file and database row is suspect until checked. The two are not the same service, and they are not priced the same way.
An infection found in a day has touched little. One that has been quietly running for months has usually spread into the database, created admin accounts and planted more than one way back in — each of which has to be found.
A known-clean backup from before the compromise turns recovery into restoration plus hardening. Without one, the site has to be cleaned in place, file by file, which is slower and needs more verification afterwards.
Sites on the same hosting account can reinfect each other. Cleaning one while its neighbours stay compromised is how sites get hacked again a week later, so the real scope is often the account, not the site.
A one-off clean with no monitoring is a smaller invoice and a larger risk. Ongoing patching, file integrity checks and alerting cost more over a year, and they are what stops the next incident rather than the last one.
Questions
If your WordPress security question is not covered here, send us the details and we will reply with a straight answer.
Do not delete anything, because the evidence of how they got in is in those files and logs. Take the site offline or into maintenance mode if it is serving malicious content to visitors, change all administrator passwords, and get in touch. We prioritise active compromises ahead of scheduled work and start triage the same day.
Most cleanups are done within a day or two. The removal itself is often the quick part; finding the entry point takes longer and matters more. Blacklist and warning removal depends on Google and your host, and usually resolves within a few days of the site being verifiably clean.
Because the entry point was never closed, or a backdoor was missed. Attackers routinely plant several, in places like the uploads directory or a database option, specifically so that a surface-level cleanup leaves them a way back. Any cleanup that does not include forensics is temporary by design.
WordPress core is well maintained and audited. The overwhelming majority of compromises come from outdated plugins and themes, weak or reused passwords, and hosting that is shared with an already-compromised site. It is an ecosystem problem far more than a core problem, and it is almost entirely preventable with patching and access control.
A security plugin is useful for firewall rules, login hardening and scanning, but it is one layer rather than a solution. It cannot save you from an unpatched plugin vulnerability, a leaked admin password or a compromised server. Patching, access control and tested backups do more for your actual risk than any plugin setting.
Yes, once you request a review and the site passes. We handle the submission through Search Console and your host after verifying the site is genuinely clean. Requesting review while anything is still infected leads to a rejection and a longer wait, so we do not rush that step.
Hardening the obvious entry points, keeping everything patched, limiting what each account can do, and monitoring so a compromise is found in hours rather than months.
The platform itself is documented at wordpress.org.
Cleaning the files is half the job. The rest is working out what was reachable, rotating every credential, meeting any notification duties, and clearing the search-engine warnings.
Related services
Start here
The more you can tell us, the more useful our first reply will be. No sales sequence — one of the people who would actually do the work reads this.
Prefer email? hello@dotance.com
We would like to use analytics cookies to understand how the site is used. They are not needed for the site to work, and nothing is loaded unless you agree. Privacy policy